This tutorial will explain how to setup and configure a DDoS protected Website. This guide assumes you have a web server and domain at the ready. This article assumes that you have the required access to update your domain name servers as well as the IP address of your backend web server (to be protected).
Guided website setup option
Open Services, choose your service's Action > Ports, and select Quick setup to open the website wizard. The wizard asks for your backend IP and connection protocol, website names, visitor HTTPS, HTTP forwarding or HTTPS redirection, and DNS provider.
For a single website, enter the Origin server IP address, choose HTTP and port 80 if your backend serves plain HTTP, and click Continue. Enter your Domain name, select Domain only, and click Continue. Choose Yes, use HTTPS, Automatic certificate, and Redirect to HTTPS for visitors, then continue. Select Use X4B DNS, review the inferred DNS zone, and click Continue. Use your own backend address and domain; choose HTTPS for the origin only when its listener expects TLS.
Choose Domain only for a specific hostname such as example.com, or Domain and all subdomains for inclusive forwarding (.example.com). AutoSSL requests an exact-domain certificate for the first option and one certificate covering the domain and immediate subdomains for the second. Compatible existing certificates are reused.
The final Review and start setup page lists every port, certificate and DNS action. First, review the website name and origin server at the top of the page.
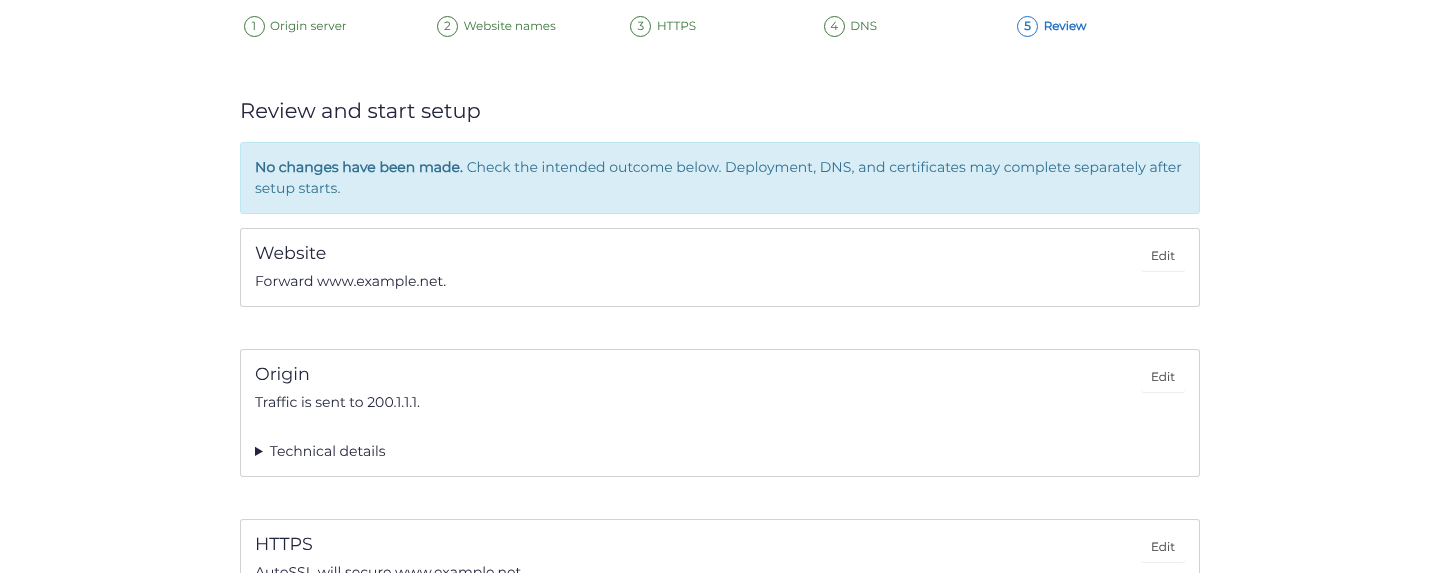
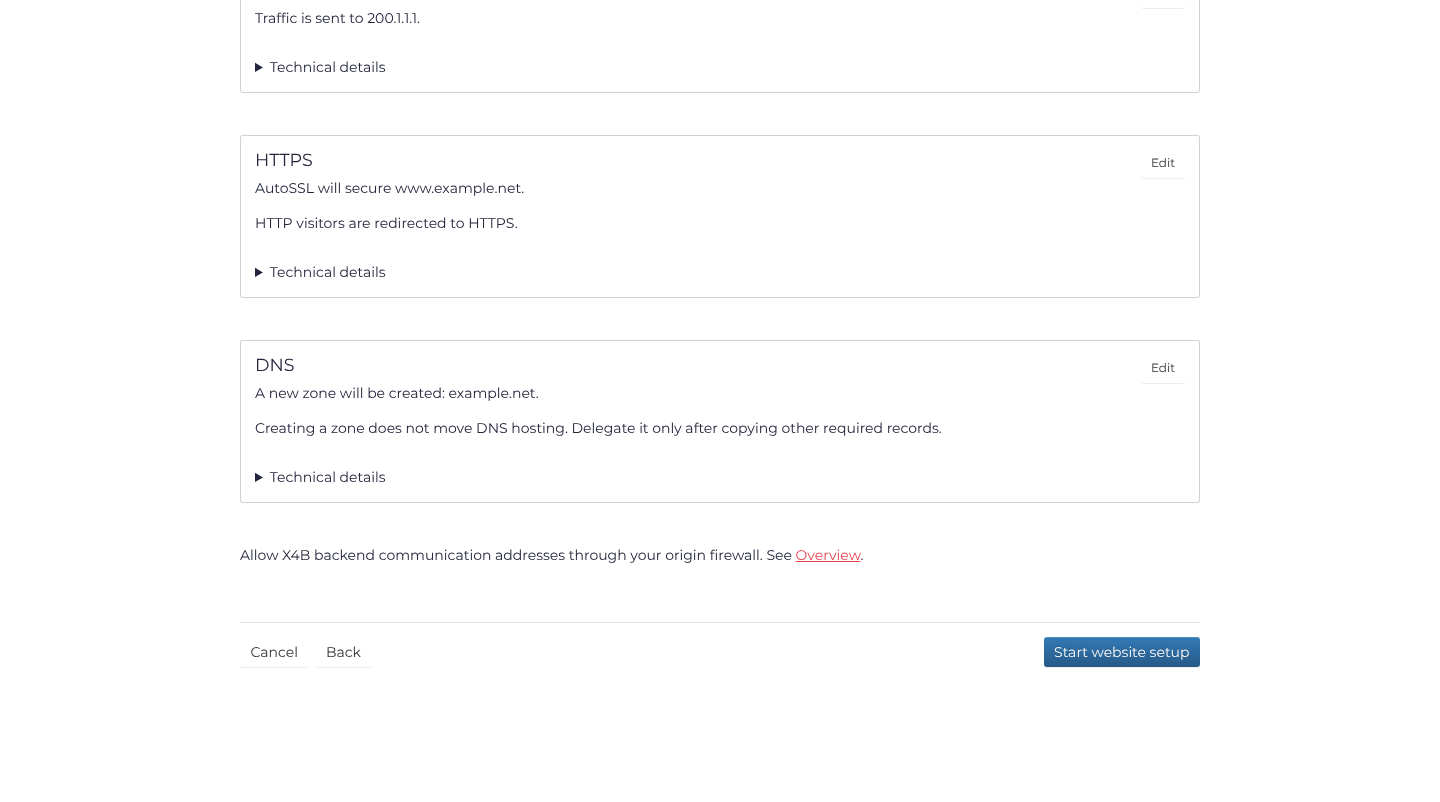
With Use X4B DNS, only missing website and certificate-validation records are added. Existing mail, TXT and unrelated records are preserved. A new zone does not move your DNS hosting: copy other required records before changing your registrar’s nameservers. For another provider, the wizard supplies the required records.
On the same review page, check automatic HTTPS, the HTTP redirect and DNS. No configuration changes are made until you click Start website setup. You can go back to edit your answers or cancel. Quick setup supports adding independent websites to configured services; it blocks conflicting ports or DNS records rather than replacing them.
For certificate coverage, deeper subdomains, and DNS validation instructions, see HTTPS / SSL.
After starting setup, choose View ports to review the saved forwarding entries. The receipt tracks deployment, DNS publication and certificates separately. Saved configuration does not mean your website is ready: wait for deployment and DNS propagation, allow backend communication through your firewall, and test the website. AutoSSL may serve a fallback certificate until issuance finishes.
Use the manual instructions below for tunnels, load balancing or more advanced configurations.
Step 1: Backend Setup
Setup your website on your server, this server will be from here on referred to as the "backend server". On the backend server you may use whichever Operating System you are most familiar with, however if unsure we recommend Debian Linux or cPanel.
Please ensure that the website is running and connectible on the backend server.
Step 2: Purchase DDoS Protection Service
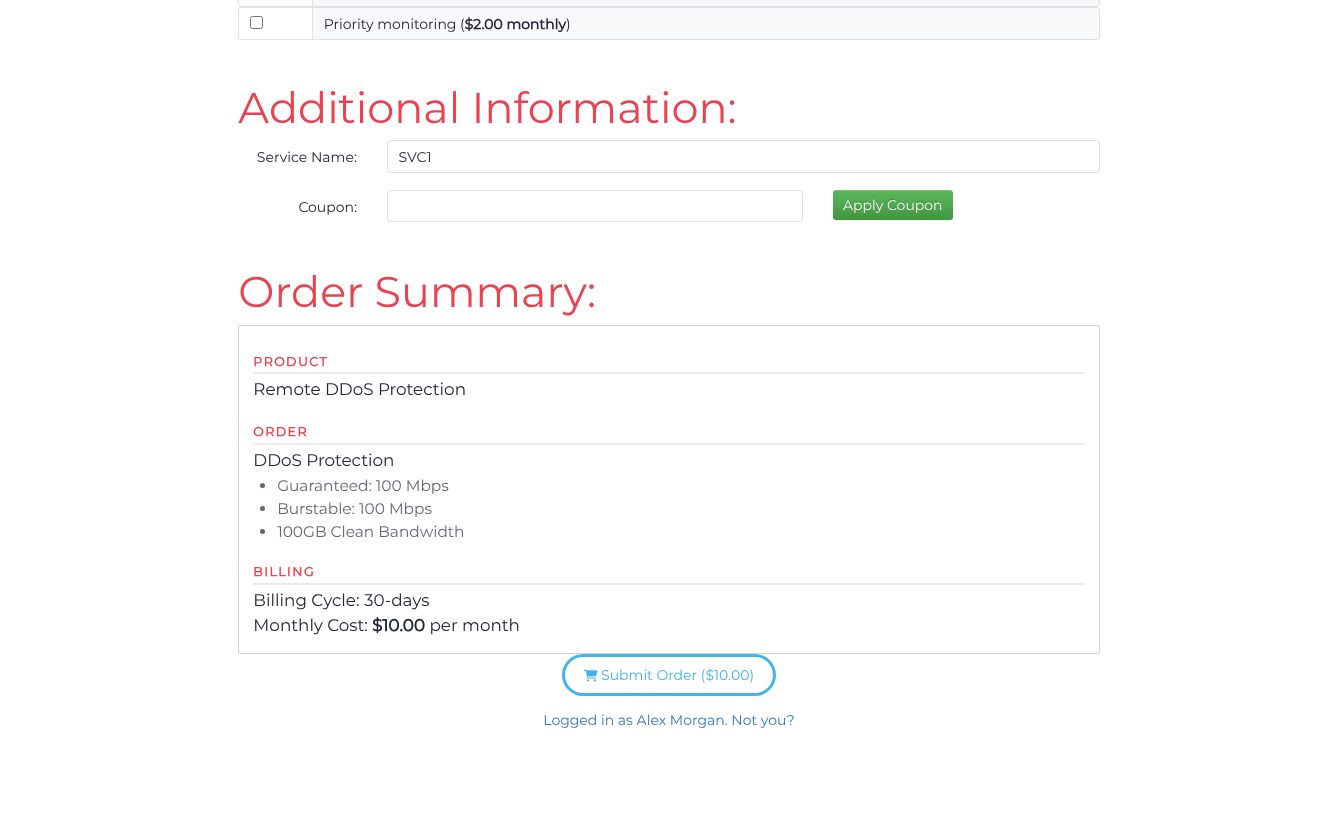
Choose a billing cycle, a service tier/network and the clean-bandwidth allowance on the DDoS protection page, then click Continue to Checkout. On Complete Order, review the filtering region when offered, enter a Service Name, and review the Order Summary before submitting your order. Choose a region close to your backend and users; clean bandwidth measures delivered traffic, not attack traffic. If you already have a suitable active service, continue with that service.
Websites can significantly benefit from the Anycast Product line for extra redundancy, protection and website loading performance.
Step 3: Encapsulation Setup (Optional)
This step is only required if you are intending to use a GRE or IP-in-IP tunnel. If you are intending to use a Reverse Proxy (RP) style connection (the easiest) then you can skip this step.
With HTTP Services the connecting clients IP is always available via the Layer 7 Client IP Forwarding technoligies. Encapsulation (such as with GRE) is usually not required but remains useful for additional security and for other more advanced applications.
An encapsulated backend requires support on the Backend Server, currently Windows and Linux Operating Systems are fully supported, with partial support for FreeBSD. Most Enterprise or even SOHO Routers also support GRE or IP-in-IP tunneling, if supported you may be able to configure the router to terminate the encapsulated network.
Open Services, find your service, and choose Action > Tunnels. Click Add Tunnel, select GRE in Tunnel type, and enter the backend server's public IP in Backend address. Retain the displayed GRE key unless your backend requires a tunnel without one, then click Save. The integrated form below is an alternative way to configure the same tunnel.
The completed example uses 203.0.113.10 as a documentation-only backend address, GRE key 1785302134, and MTU 1472. Replace the backend address with your server’s public IP and use the same key and MTU when configuring that server.
After saving a port that uses this tunnel in Step 4, return to Tunnels and choose the tunnel's Action > Setup Tunnel. Select Linux / BSD and Download Tunnel Script, or Microsoft Windows and Download Application, as appropriate for your backend. The tunnel must be referenced by an Encapsulated port before it is usable. Install the downloaded script or application on your backend using the linked operating-system instructions.
Step 4: Add Ports
Add the ports required to run your service. In this case, the default port for HTTP servers is port 80 (All HTTP traffic occurs over TCP). If unsure you can determine what port(s) the service bound to by using the ss or netstat commands as appropriate.
Open Services, find your service, and choose Action > Ports. Under Single Port, click Add port manually when Add your first port is shown; otherwise click Add Port. Enter the public port in Port start, choose the documented Protocol, and set Backend method to Reverse Proxy with your Backend address and Backend port, or to the available Encapsulated method with the tunnel created in Step 3. Click Save after each new entry and check the saved row. For a range, choose Port Range > Add Port Range, enter Port start and Port end, then select the protocol and backend before saving.
The completed example uses 203.0.113.10 as a documentation-only backend address. Replace it with your backend address, or select the GRE tunnel you created when using encapsulation.
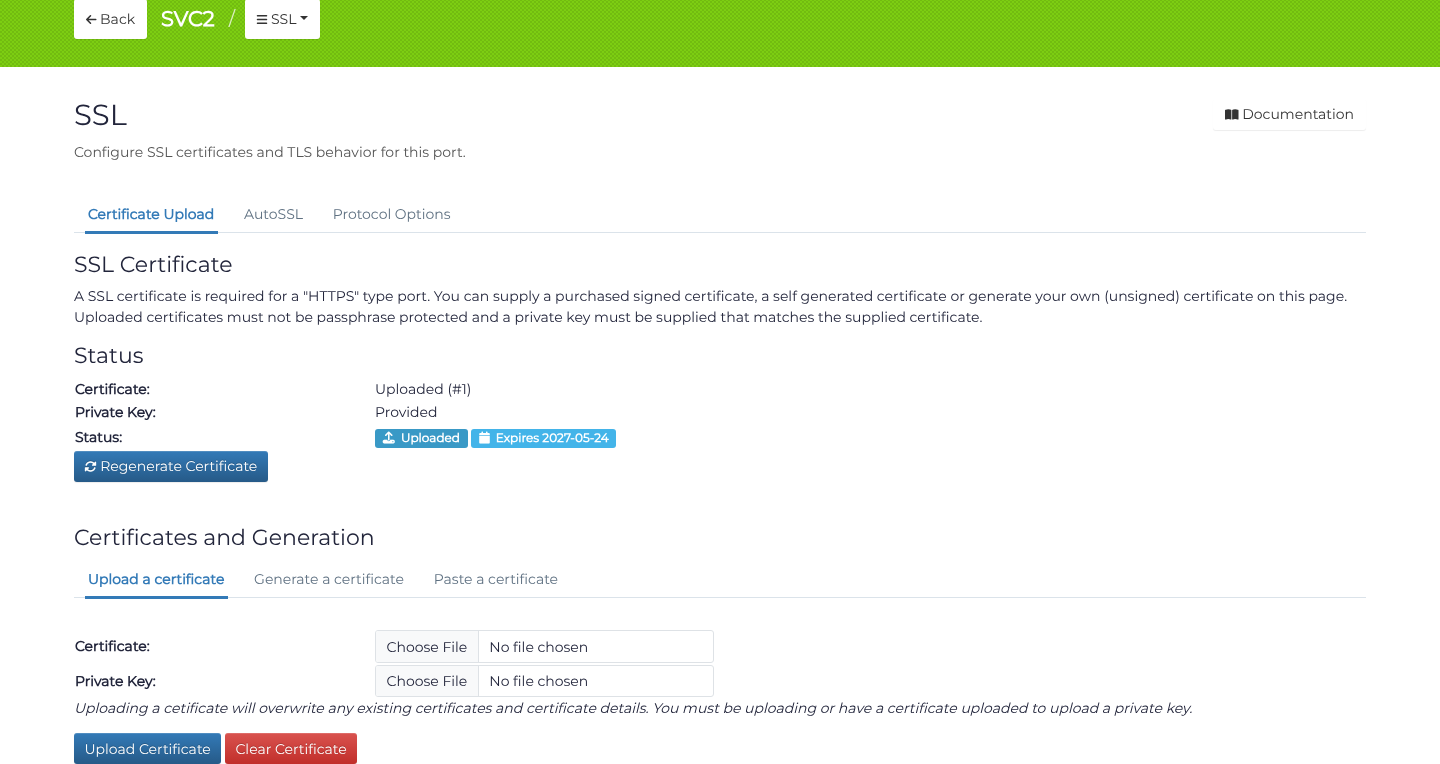
You may also wish to add port 443 (HTTPS). First add this port, making sure to select HTTPS as the port protocol. Open its Action > SSL page, choose Certificate Upload > Upload a certificate, select the Certificate file and matching Private key file, and click Upload Certificate. Check that the certificate status is Uploaded and the private key is Provided. For certificate alternatives and further configuration, see HTTPS and SSL.
If you have a region field on your service (Anycast services) then for most configurations this should be All.
If you have HTTPS configured on your web server and wish for the backend connection to be made over SSL then select the padlock in the backend section and use the SSL port (most likely 443). Otherwise you may point the port at your backend server with a backend port of 80 (no padlock selected). An example of a setup can be seen in the interactive form below.
Step 5: DNS
For this step you may use either our DNS service or a third party DNS provider. In either case the aim is point your website (via DNS) at the DDoS Protected IP address. This step assumes you are configuring a domain name, if this does not apply you may skip this step (or replace it).
For more information on DNS see this article on the basics of DNS.
Option 1: X4B DNS
Our provided DNS hosting is available as the DNS page in the dashboard.
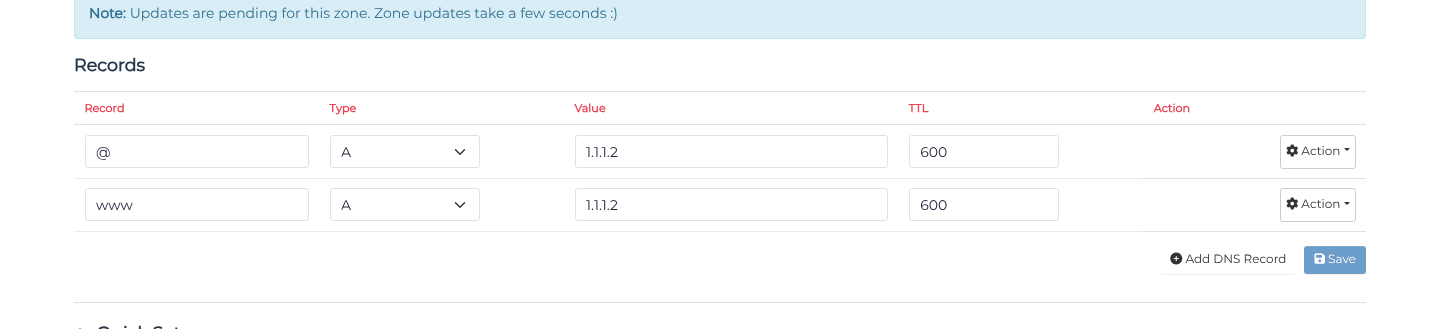
On DNS, enter your domain under Add DNS Zone and click Add Zone. Open the new zone, click Add DNS Record, choose A, enter @ for the zone apex and your Filtered IP as the value, then click Save. Add a separate record for each hostname you serve, such as www. Use AAAA only for a configured protected IPv6 path.
Before changing your registrar's nameservers, copy every required record to the new zone and verify its answers with dig. Use the nameservers displayed in the Dashboard. DNS caches and delegation changes take time to propagate; see DNS propagation.
You will need to configure your domain name to use our nameservers, these can be found in the DNS Management page of the Dashboard.
Option 2: Third Party DNS Provider
You can find the options required for configuration on the service Overview page (Action > Overview). You will need to enter these settings into your provider. If you have a single homed service you may alternately be able to use the proxy IP in A records directly but certain features will not be available.
Unfortunately we are unable to provide tutorials for all Registrars and 3rd Party DNS services. If you are unable to find the one you need then you will need to extrapolate the values provided on the Information Page or on the Page after purchase as needed.
We recommend reviewing the tutorial for another company as it may provide the insight you require. Your Nameserver company / service may have help resources that can assist you in this matter.
If you need assistance related to our services, or information not specific to the 3rd party service you have chosen feel free to ask our friendly staff via a Support Ticket. While we likely can't help you with the specifics of your registrar, phrase us a generic question (i.e "I have the options X and Y which do I need") and we can likely help.
Step 6: Finish & Test
Once all steps are completed and the progress bar for deployment of the configuration reaches 100% you should be able to connect to your website on your Filtered IP.
This Filtered IP is the address that you should use in any DNS names, or supply to any connecting users. All traffic which arrives at configured ports on a Filtered IP will be filtered for attack, and then forwarded to your configured backend server.
Note: If you or your network provider run a firewall, allow the service’s Backend Communication addresses only for the protocols and backend ports you have configured. Keep other firewall rules in place. See Adding a firewall exception, and ask your provider to apply the required rule if they manage the firewall. Do not disable the firewall to test connectivity.
Additional Information
Additional Headers
Layer 7 headers exist that provide information on:
- the request Scheme
X-Scheme - the source server
X-Source - the client IP
X-Real-IP(can be overridden) - the request UUID (disabled by default)
Apache 2 compatibility
If you are using Apache 2.4.65 or later as your backend server with a backend of HTTPS you will need to have the backend SNI Pool mode set to "SNI Pool" for compatibility. This is because Apache2 2.4.65+ enforces SNI on all HTTPS connections. When creating a port with a HTTPS backend server the default is to set this automatically. For existing ports you can change this in the HTTP Options section of the port configuration as detailed in the HTTP Options documentation.
Frequently Asked Questions
Help I can't connect to FTP! or how do I connect to SSH?
Connect to your non-public services using your normal, non DDoS protected backend IP. You can also choose to forward FTP or SSH over the protected IP, but this is not recommended. By restricting access to targeted brute force or exploit attacks you gain a significant amount of security.
Can I use third party Web Accelerator services with this protection?
We do not officially support any third-party web accelerator services (such as CloudFlare). At the very least to prevent mitigation issues ensure that the Accelerator service supports HTTP Keepalive and that the appropriate settings for Client-IP forwarding are configured in the HTTP Options section of the X4B port interface.
Enhanced HTTP Filtering is not compatible with any form of Web Accelerator service.
How do I get the real IP of a visitor to my website?
When using a Layer 7 reverse proxy service the connection will originate from an appropriate backend communication address on our end. We will provide the connecting clients "Real IP" in an HTTP header, in our case we use the X-Real-IP header. You can find an article on this and some example set up instructions for various web servers here.
How many domain names (or other resource) can I configure?
All resources are fair use with high limits you are unlikely to ever see.
What ports can I use? Can I access the IP directly or do I need a domain name?
Yes. The filtered IP we provide is your IP, you can setup the service however you desire and use the service (within the terms of the AUP/TOS) however you like. Any restrictions enforced by us (outside of fair use) are minimal and largely driven by technical limitations.
